

Technical and organizational measures (TOM)
As of August 18, 2026
These technical and organizational measures apply to Netstream AG and Netstream Cloud AG.
Subject of the document
This document summarizes the technical and organizational measures as defined in Article 8, paragraph 1 of the GDPR. It describes the measures taken by the data controllers to protect personal data.
The measures are embedded in a certified Information SecurityagSystem (ISMS) according to ISO/IEC 27001:2022 and are based on the protection goals of confidentiality, integrity, availability and resilience.
1. Confidentiality
1.1 Access control
Measures to prevent unauthorizedagto data processing facilities.
- Automatic access control system with electronic locking system and individual authorizationag
- Biometric access controls in data centers
- Video surveillance in security-relevant areas
- Doorbellagwith camera in office premises
- Restrictive access policies and security personnel
- Key system with documented key book
- Visitor escort only by authorized staff
- Alarm systems at all relevant entrances
- agsafeguards with service providers including confidentiality agreements
- Careful selection of cleaning staff andaginsurance
- Home office policy with defined security requirements
1.2 Access control
Measures to prevent unauthorized use of data processing systems.
- Personal authentication with username and password according to recognized industry standards
- Central password policy with complexity requirements and regular changes
- Two-factor authentication (2FA) for all supported systems
- Central passwordagfor secure management of all access data
- Endpoint Detection and Response (EDR) on all managed endpoints
- Use of firewalls and network segmentation
- Encrypted Wi-Fi according to the latest standard with a separate guest network
- VPN required for all remote access
- Full encryption of mobile storage devices and notebooks
- Remote wipe capability for mobile devices in case of loss or theft
- Automatic desktop lock after inactivity
- Automatic account lockout afteraglogin attempts
- Deactivating inactive accounts
- Separate accounts for administrative tasks
1.3 Access control
Measures that ensure that access is only granted to authorized data.
- Role-based access control with a documented authorization concept
- Minimal rights allocation based on the need-to-use principle
- Logging of access to applications, especially when data is entered, modified and deleted
- Regular review of access permissions
- Professional destruction of data carriers and files
- Physical erasure of data carriers before their reuse
- Secure storage of data carriers in accordance with the Clean Desk / Clear Desk Policy
- Regulated withdrawal of access rights upon leaving or changing roles
1.4 Separation control
Measures to ensure that data collected for different purposes is processed separately.
- Strict separation of production and test environments
- Logical client separation in all relevant applications
- Network segmentation with defined security zones
- Differentiated authorization concept with definition of database rights
1.5 Pseudonymization and data minimization
- Principle of data minimization in every data collection
- Anonymization/pseudonymization of personal data upon transfer or after the expiry of the retention period
- Data masking for test data; exceptions are documented in the exceptionag
2. Integrity
2.1 Control of further disclosure
Measures that ensure that data is not read, copied, modified or removed without authorization duringagor storage.
- Encrypted dataagaccording to current industry standards
- Encryption of data at rest according to recognized cryptographic standards
- VPN tunnel for remote access to internal resources
- Data is provided exclusively via encrypted connections
- Do not send sensitive data via email; use secure file-sharing platforms
- Documentation of data recipients and retention periods
- Supplier managementagto ISO 27001 with regular review
- Automated monitoring of cryptographic configurations
2.2 Input control
Measures that ensure it can be subsequently verified whether and by whom data has been entered, changed or removed.
- Logging of data entry, modification, and deletion
- Traceability through individual usernames
- Central logging infrastructure with tamper-proof storage
- Defined minimum retention periods for logs
- Access to logs is restricted to authorized personnel only
- Regular monitoring and analysis of the protocols
3. Availability and resilience
3.1 Availability control
Measures that ensure personal data is protected against accidental destruction or loss.
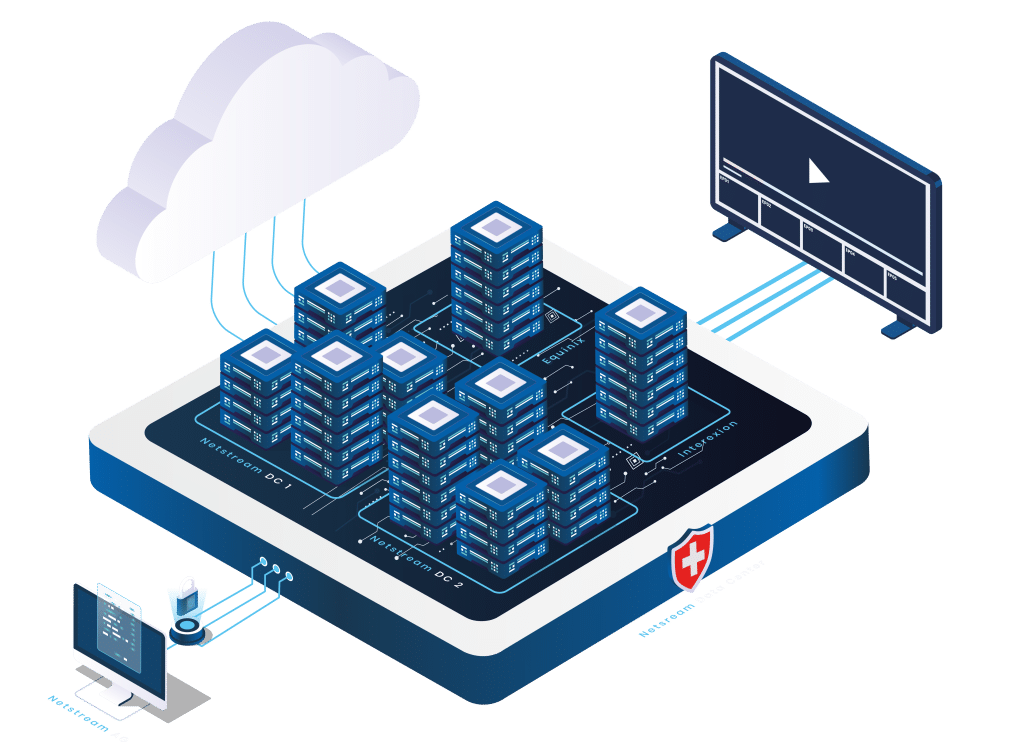
- Data centers whose design is based on Tier IV standards, with full redundancy
- Fire and smokeagsystems as well as automatic extinguishingag
- Climate monitoring in server rooms
- Uninterruptible power supply (UPS) with emergency powerag
- Redundant network feeds
- Redundancy architecture for all business-critical services
- Monitoring and planning of system capacities to avoid bottlenecks
- Regular automated Backupwith encrypted storage
- Store data backups in a secure, out-agthe-way location
- Documented Backupand recovery concept with regular tests
- Automated monitoring systems with early warning and escalation processes
- On-call organization for timely response to system malfunctions
- Documented emergency plan with regular testing
- Incidentagprocess with defined escalation levels
4. Procedures for regular review, assessment and evaluation
4.1 Information security and data protection
- Certified ISMS according to ISO/IEC 27001:2022
- Internal Information Securityag(CISO)
- External Data Protection Consultant
- All employees are obligated to maintain data secrecy
- Regular training in data protection and information security
- Regular awarenessagincluding simulated phishing tests
- Maintaining a record of processing activities (Art. 12 GDPR)
- Systematic riskagwith documented risk analysis and treatment
- Classification of all information according to a defined scheme
- Guideline for the safe use of AI systems
- Regular internal and external audits
- Annualagreview with target definition and KPI measurement
- Compliance with the information obligations pursuant to Art. 19 et seq. GDPR
4.2 Incident responseag
- Documented incidentagwith defined escalation levels
- Reporting process for data breaches to the FDPIC (Art. 24 para. 1 DSG) and data subjects (Art. 24 para. 4 DSG)
- Involvement of the data protection advisor in data protection incidents
- Endpoint Detection and Response (EDR) on managed endpoints
- Firewalls with network segmentation
- Regular updates of all systems and applications
- Vulnerabilityagwith systematic recording, evaluation and remediation
- Securing evidence in a tamper-proof environment
- Lessons Learned from Security Incidents
4.3 Privacy-friendly default settings
- Employee training in Privacy by Design and Privacy by Default
- Data collection is limited to the minimum necessary for the purpose
- Requirements for secure software development and code review
- Data masking and anonymization for test data
4.4agcontrol
- Written instructions toagthroughagprocessing agreements
- Careful selection ofagwith documented evaluation
- Ongoing review and regular auditing of suppliers
- Non-disclosure agreements for suppliers with access to confidential information
- Ensuring data destruction after completion of theag
- Contractors' obligation toagdata secrecy